
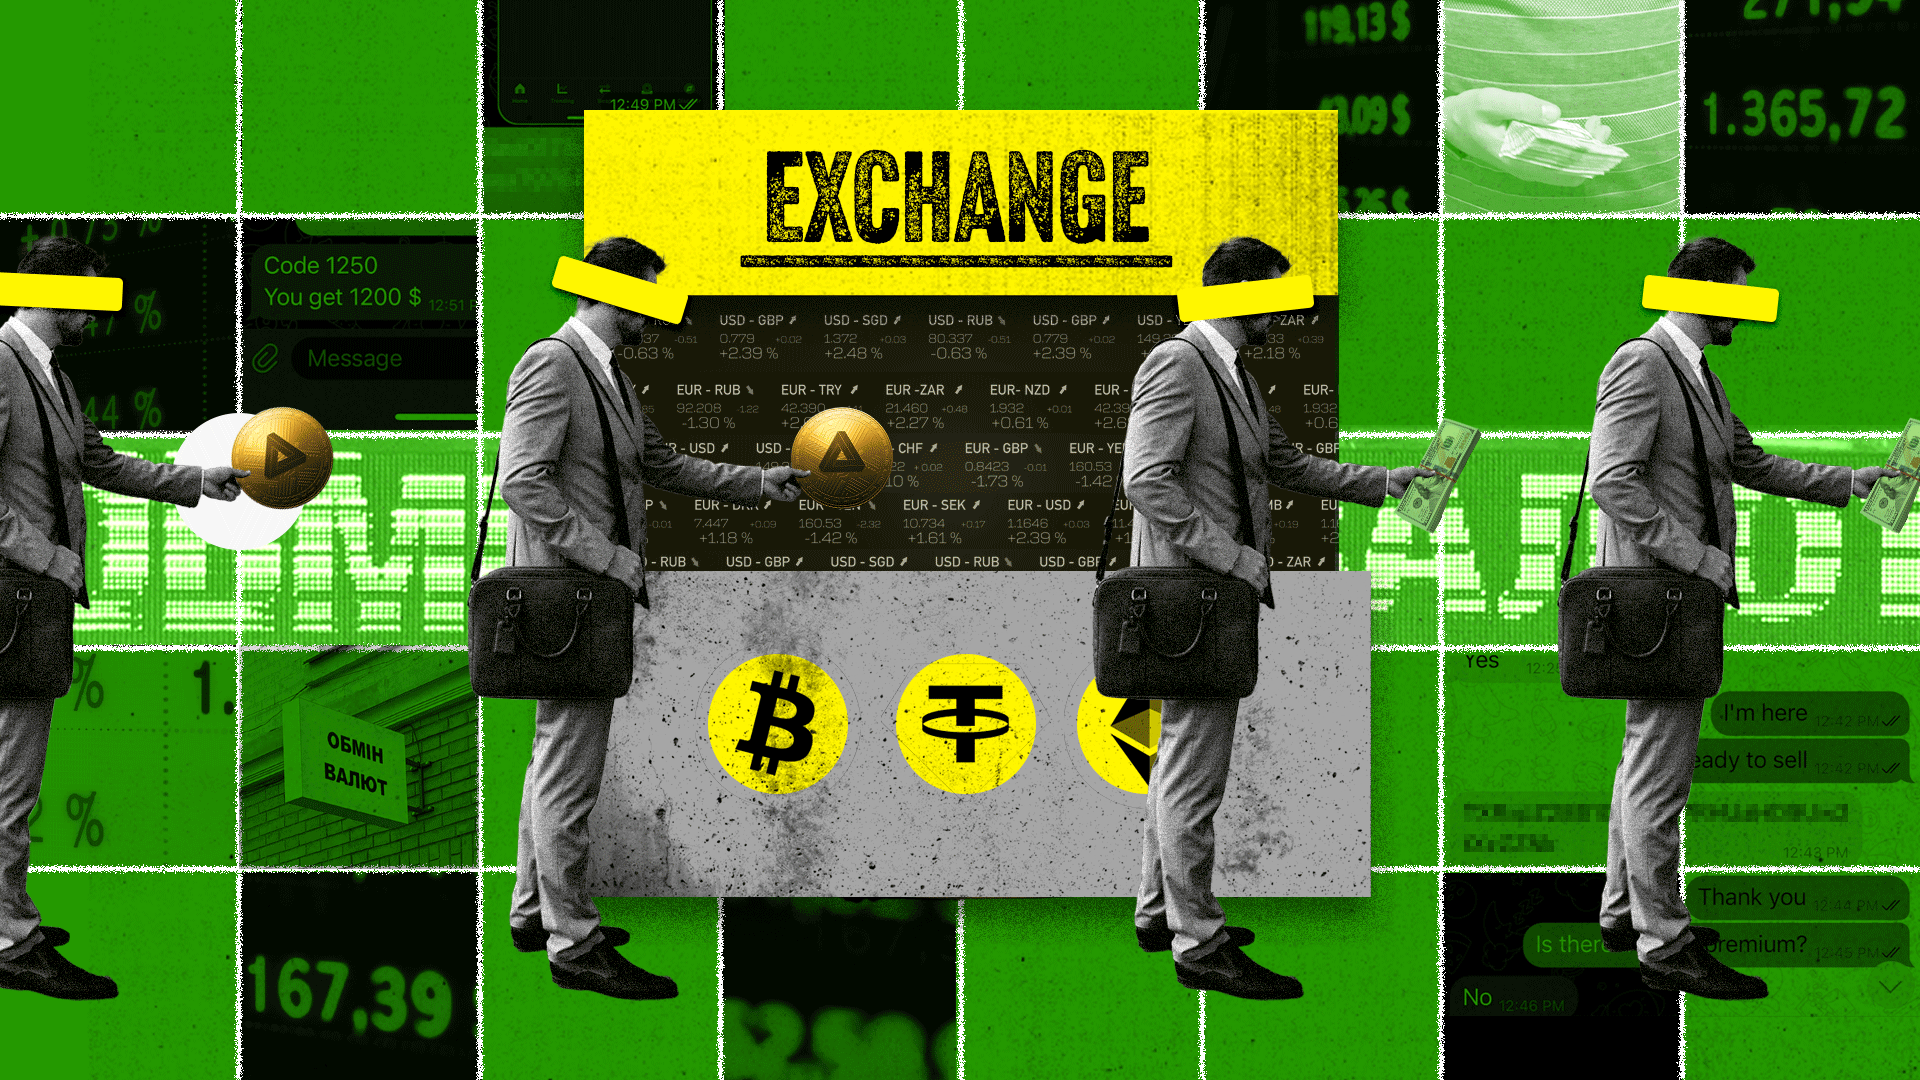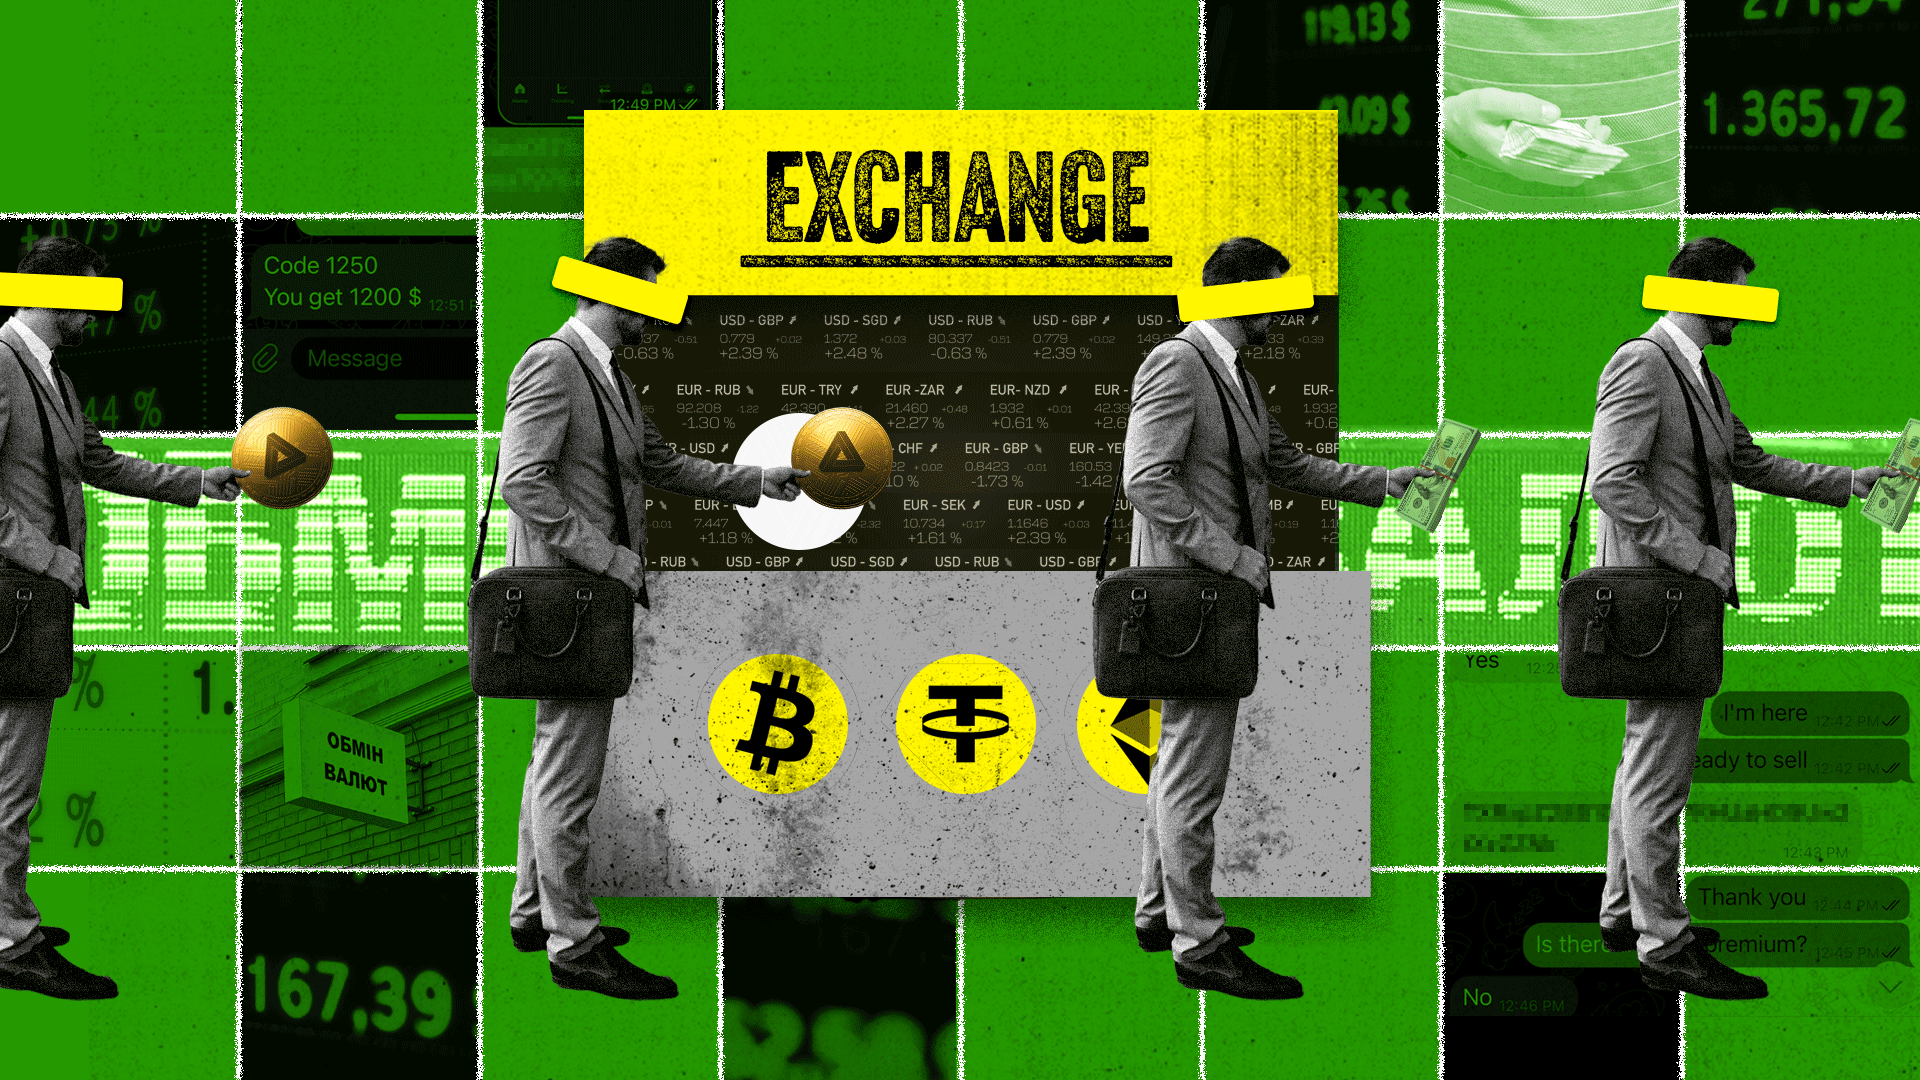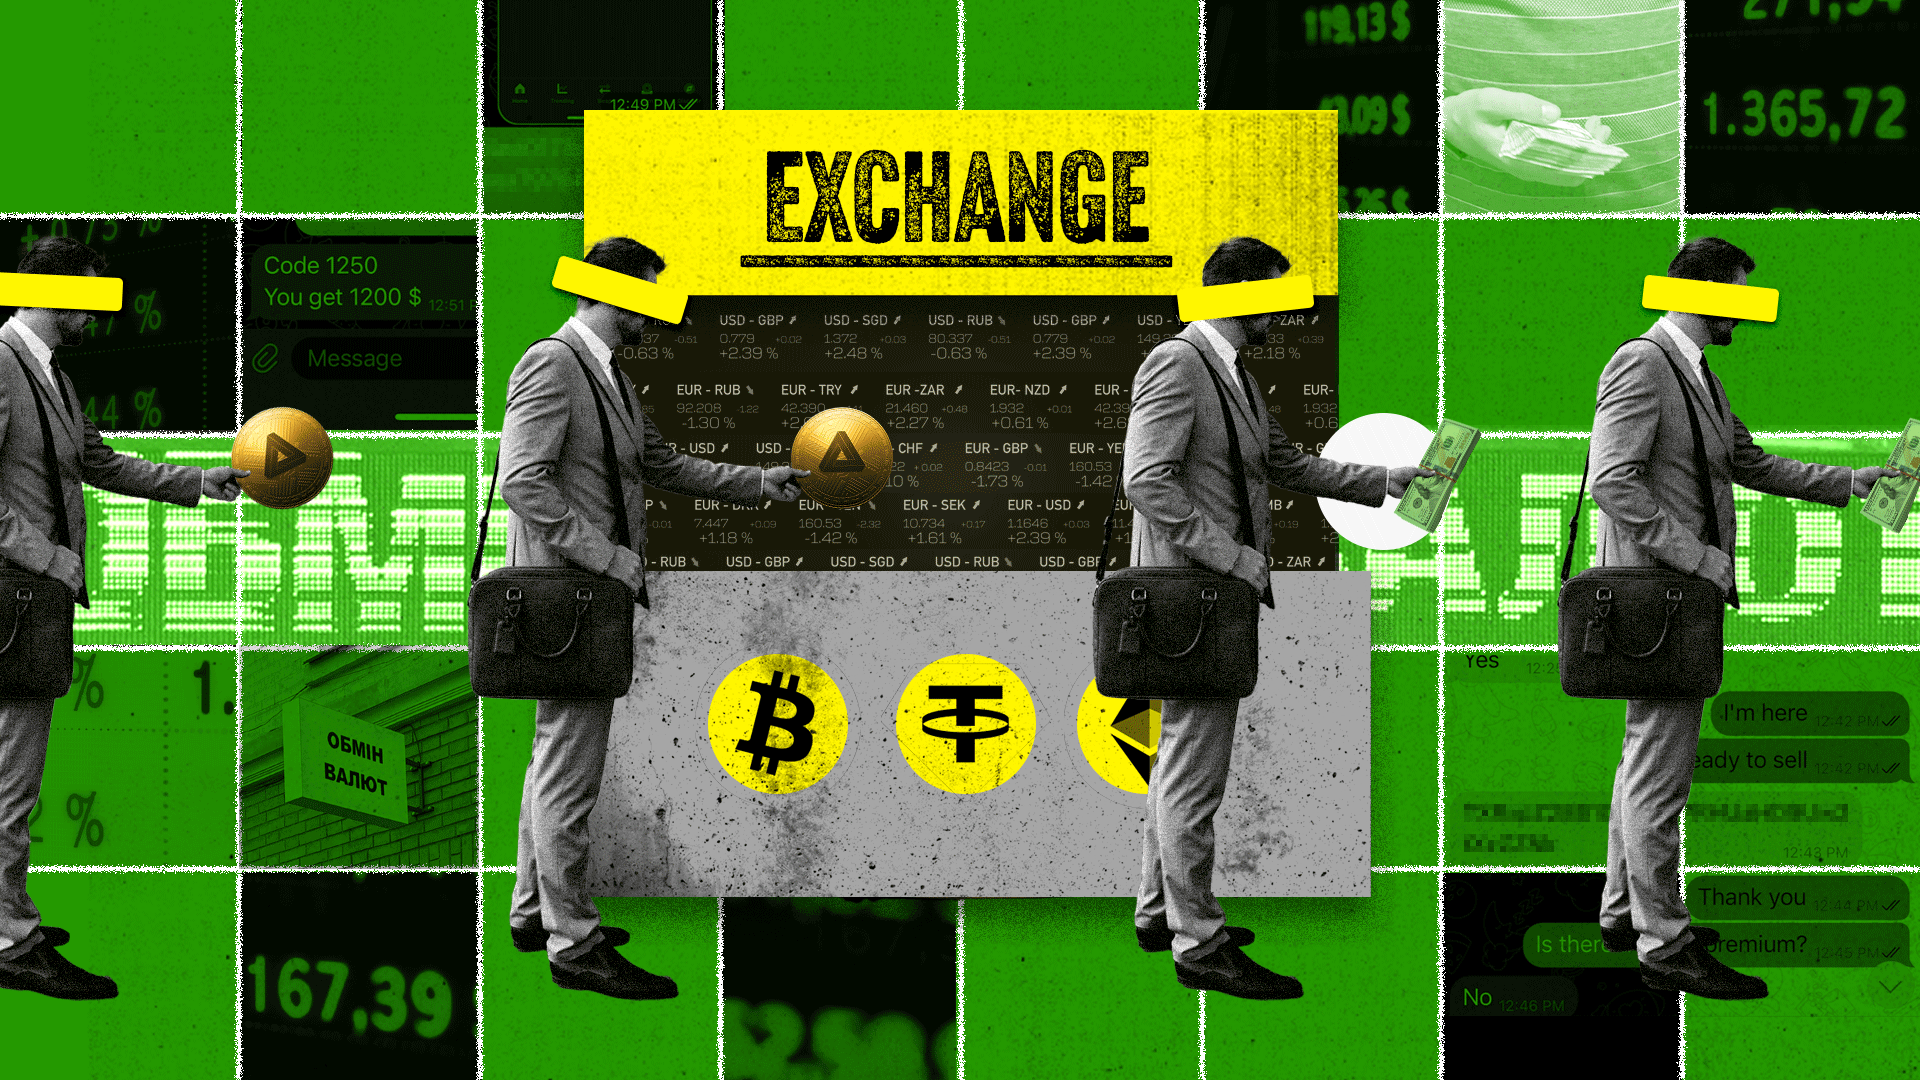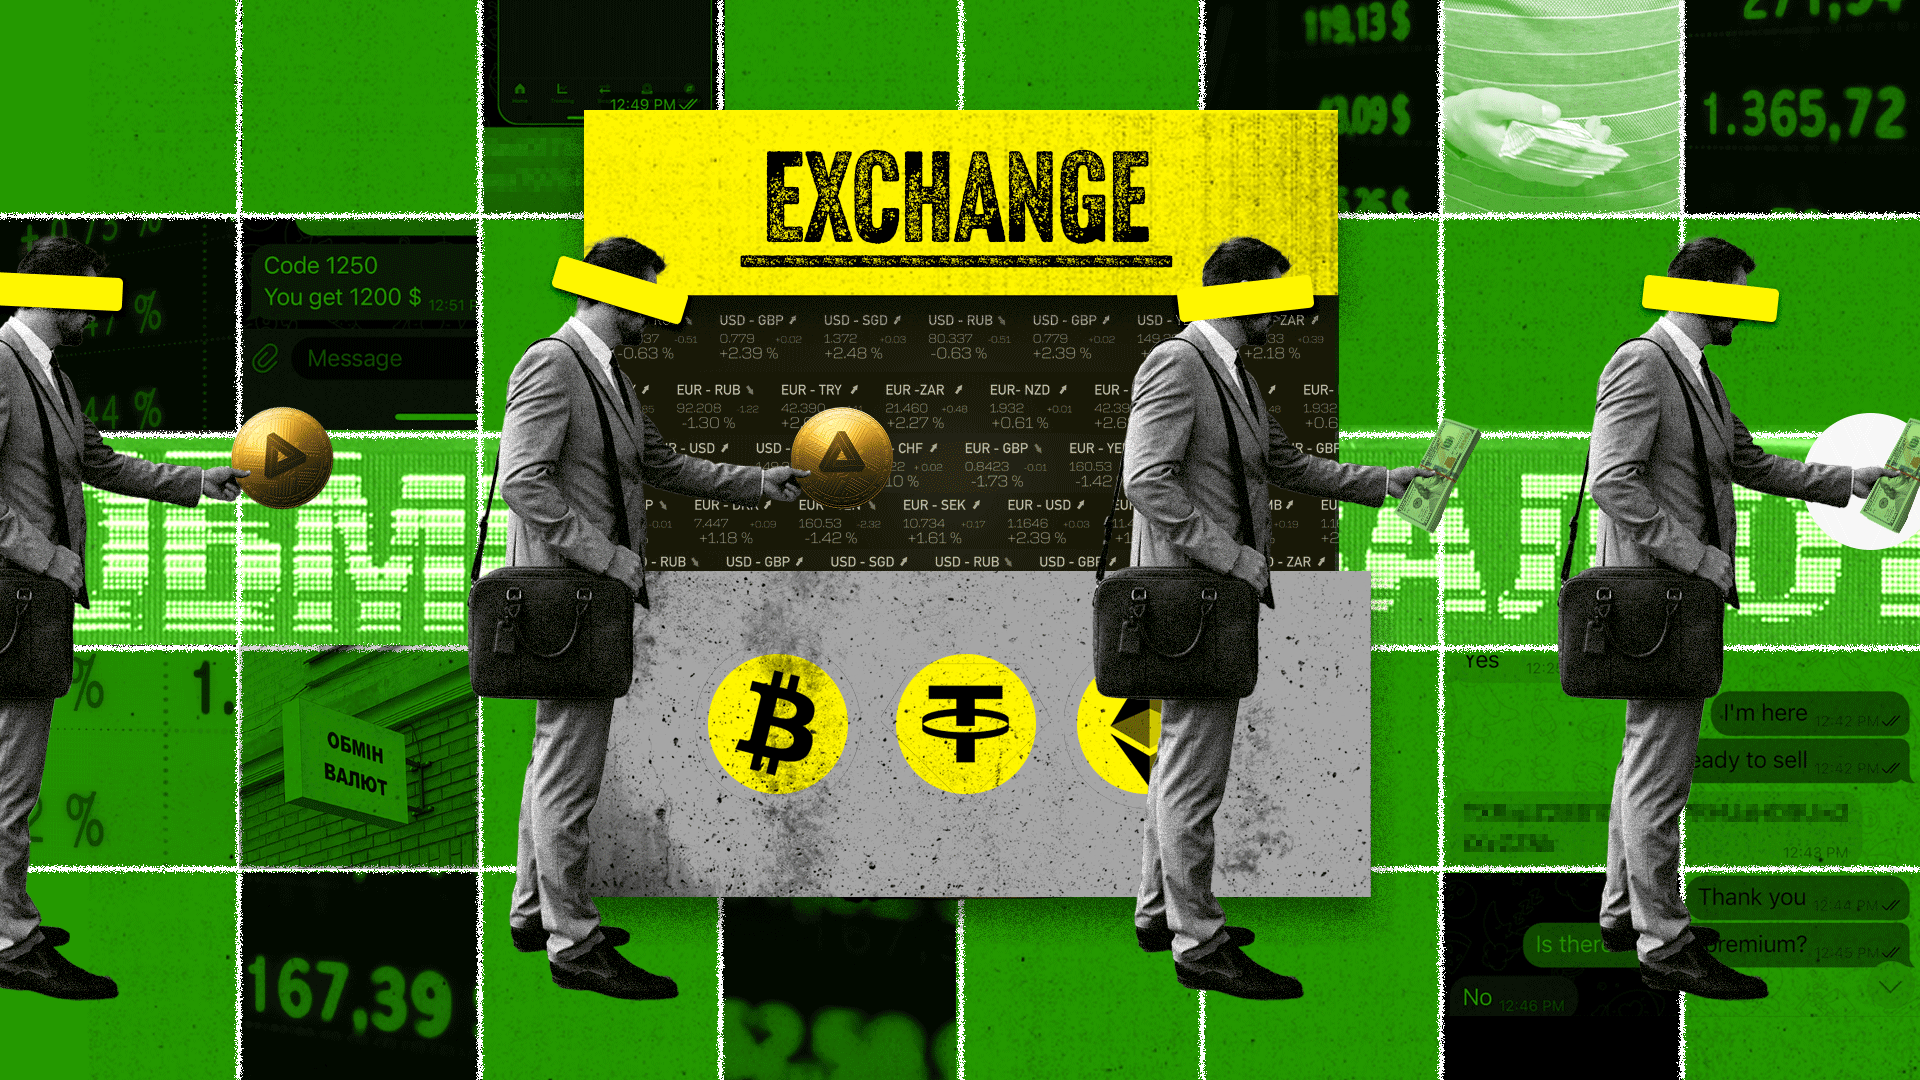
A hacking group linked by authorities to North Korea used fake IT jobs, AI face swapping and malicious software to target thousands of people and steal cryptocurrency.
WEBDESK | MEDIABITES
A hacking group known as WaterPlum has stolen an estimated $10.71 million in cryptocurrency from 7,000 accounts after targeting IT professionals with fake job advertisements, according to cybersecurity authorities in the United States, Japan, Germany, and Australia.
Authorities said the group infiltrated at least 30,000 devices between December 2025 and July 2026 as part of a campaign targeting software developers and other technology professionals.
WaterPlum allegedly posed as an employer offering legitimate-looking jobs to applicants in hundreds of countries. During the recruitment process, applicants were instructed to download files presented as alternatives to popular video conferencing applications such as Zoom.
Cybersecurity officials said the files were used to compromise victims’ devices and obtain sensitive information.
The group also allegedly used another method involving fake North Korean IT workers who secured positions at companies. During online interviews, members reportedly used artificial intelligence-powered face-swapping technology to disguise their identities.
The individuals would then ask interviewers to turn off their cameras, claiming they were experiencing network problems.
Authorities said the operation enabled the group to access corporate environments and individual devices.
Laptop farms helped conceal locations
Japanese authorities reportedly uncovered evidence of WaterPlum’s activities after identifying a so-called laptop farm, a setup used to make remote workers appear to be operating from another location.
Investigators found evidence that millions of dollars in cryptocurrency had been transferred to locations outside Japan.
The people associated with the laptop farms were reportedly located mainly in North Korea, China and Russia, with smaller numbers in Africa and Southeast Asia.
Authorities also said WaterPlum obtained identity documents, passwords and other sensitive information from thousands of people. Such information could potentially be used for extortion.
The group has been linked by authorities to the 313 General Bureau of the Munitions Industry Department, which is subordinate to the Central Committee of the Workers’ Party of Korea.
Fake workers and crypto theft
Cybersecurity experts have warned for several years about North Korean operators using fake identities to obtain technology jobs.
Andrew Cullen, a University of Melbourne cybersecurity and artificial intelligence specialist, said reports of fake North Korean employees had been appearing for three to four years, but the activity appeared to be accelerating.
He said the scale of infiltration was difficult to determine because companies do not always disclose when they discover that workers have used false identities.
The WaterPlum campaign comes amid broader concerns about North Korean cyber operations targeting cryptocurrency.
The FBI has previously attributed a $1.5 billion cryptocurrency theft from Bybit to North Korean state-sponsored hackers.
AI could accelerate cyberattacks
Cullen said artificial intelligence could make cyberattacks more frequent and allow criminal groups to operate at greater speed and scale.
AI tools can help attackers communicate with more people, maintain conversations, organize information and make fraudulent interactions appear more natural.
AI is also being examined in connection with ransomware operations, in which attackers lock victims out of their computer systems and demand payment to restore access.
Cullen said AI could potentially automate parts of the extortion process, reducing the amount of direct human involvement required by attackers.
How people and companies can protect themselves
Cybersecurity specialists recommend basic precautions including regularly changing passwords, keeping devices and software updated and avoiding suspicious links and downloads.
Employers can also take additional steps when hiring remote workers, particularly for sensitive technology positions.
Cullen recommended that companies verify the identities of remote employees through direct interaction, preferably in person.
He said the fundamental cybersecurity advice has remained largely unchanged, but the volume and speed of attacks have increased.
The latest campaign highlights the growing challenge for individuals and businesses as cybercriminals combine traditional social engineering techniques with artificial intelligence and cryptocurrency theft.